01
AI Security
AI & Agent Security
Security of AI agents and tool-calling workflows against prompt injection and unsafe tool usage, through red-team driven attack simulation and policy enforcement.
LLMs · Prompt injection · Red teamingSanil Grover
Cybersecurity Researcher/B.Tech CSE, Thapar '27
Former security intern at I4C (Ministry of Home Affairs) and eSecForte, where I worked on cloud security. Now exploring AI agent security. AWS Certified Solutions Architect – Associate. B.Tech CSE, Thapar, class of 2027.
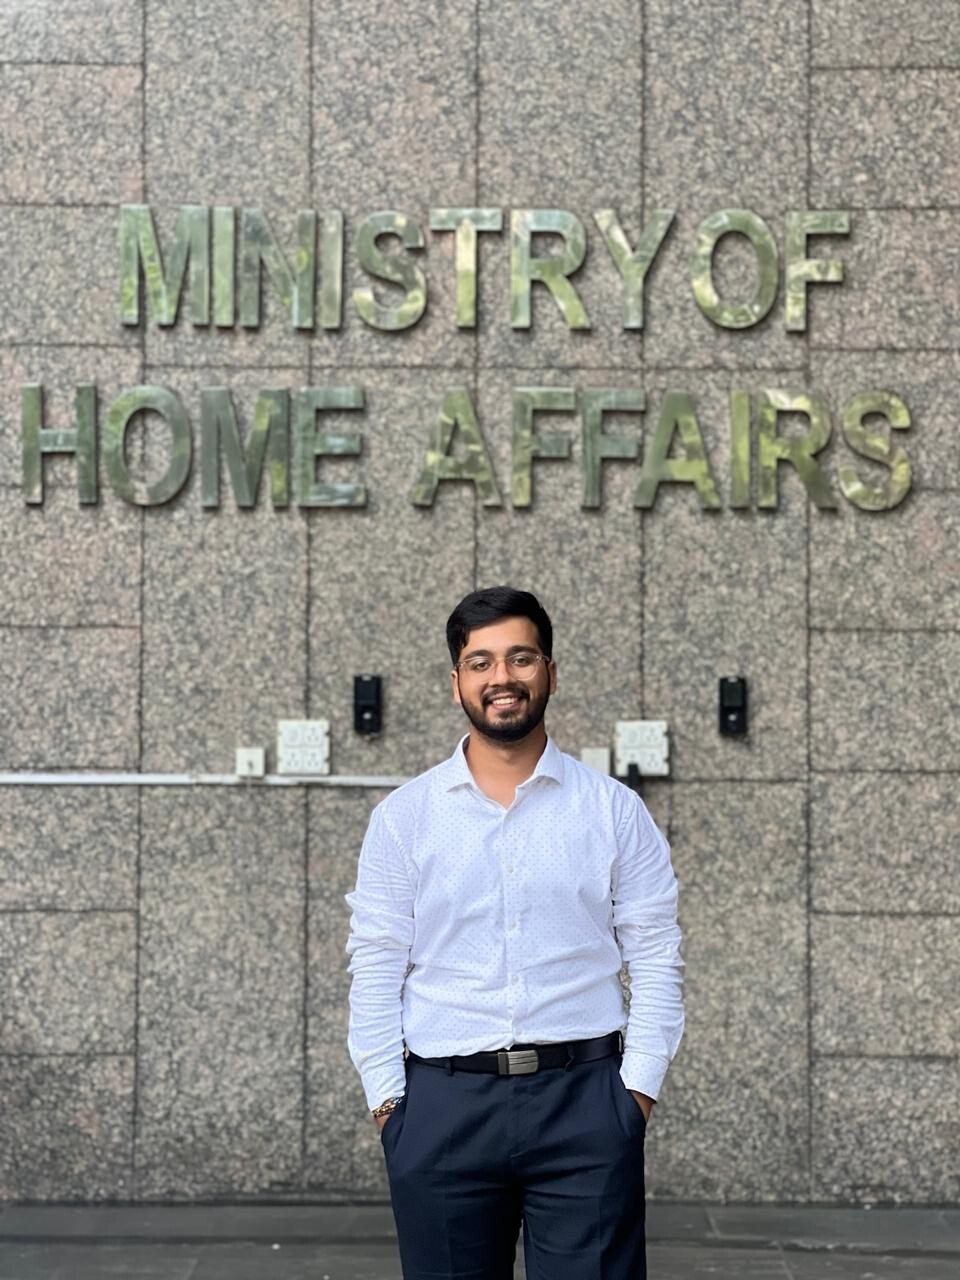
that's me → more of the same
Recommendations
Recommendations from colleagues, mentors, and internship supervisors will appear here as they come in.
Leave a recommendationKnow me? Leave a recommendation →
Why I do this
Third-year CS student at Thapar who ended up doing malware analysis at the Ministry of Home Affairs before fully knowing what JADX was. That internship did more for my understanding of how threats actually work than any course has.
Most of my time goes into figuring out how systems behave under adversarial conditions, whether that's a malicious APK hiding its intent behind layers of obfuscation, an AI agent being coaxed into doing something unintended, or a deepfake detection pipeline I can actually trust.
The rabbit holes
Three threads run through everything on this site. Each one is backed by the internships, projects, and tooling detailed below.
01
Security of AI agents and tool-calling workflows against prompt injection and unsafe tool usage, through red-team driven attack simulation and policy enforcement.
LLMs · Prompt injection · Red teaming02
Static triage and dynamic instrumentation of malicious Android APKs: payload droppers, boot-receiver persistence, and C2 infrastructure disguised as legitimate API endpoints.
MobSF · JADX · APKTool · Frida · VirusTotalCloud security assessments across AWS resources: security misconfigurations, IAM and access-control weaknesses, and compliance gaps.
AWS · IAM · SAA-C03 certifiedApplication-layer testing across the OWASP Top 10: SQL injection, SSRF, path traversal, file upload flaws, and OS command injection.
Burp Suite · HTTP Toolkit · PortSwigger labsVulnerability assessment plus hands-on enterprise networking: DHCP, subnetting, static/dynamic routing, firewall and proxy policies, NAT/PAT, and VLANs.
Nmap · Nessus · PCAPdroid · Searchsploit03
Reconnaissance on fraudulent infrastructure and investigation support during active cybercrime casework at I4C.
Nmap · ffuf · dirb · Exploit DBTwo papers presented at ICAAV 2026, the International Conference on Autonomous Aerial Vehicles (ADE-DRDO & AeSI), on UAV swarm identification and propulsion-system degradation modeling.
Read the researchThings I've broken on purpose
Two pieces of work that best represent what I build. The full set lives on the projects page.
Where I've worked
2026Jun – Jul
Cloud security assessments across AWS: misconfigurations, IAM and access-control gaps.
2025Jun – Aug
Reverse-engineered 20+ malicious Android APKs, uncovering payload droppers, persistence, and C2 infrastructure.
2024Jun – Jul
Vulnerability assessments with Nmap and Nessus; OWASP Top 10 labs in Burp Suite.
Research & writing
Conference work presented at ICAAV 2026, the International Conference on Autonomous Aerial Vehicles (ADE-DRDO & AeSI), alongside notes written between coursework and deadlines.
Chapter & community
OWASPChapter
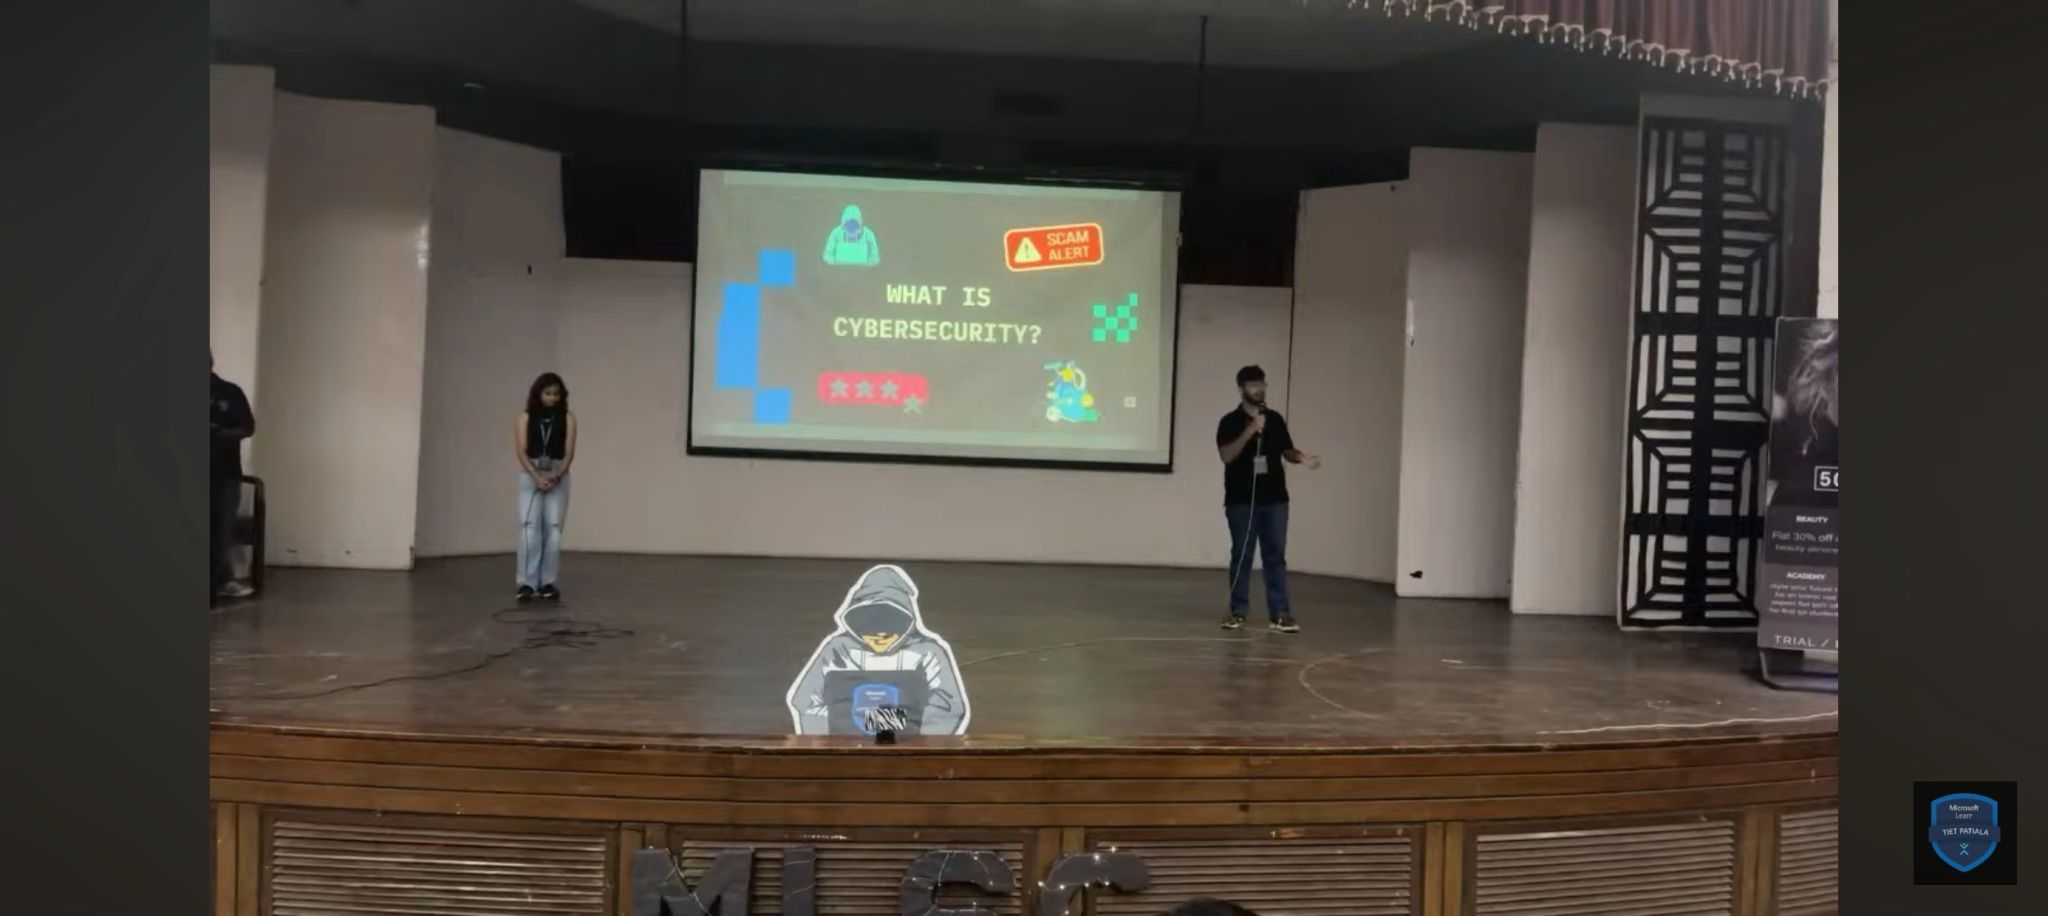
MLSCMember
Technical arsenal
The tools and technologies behind the threads above. No progress bars. The work is the evidence.
Outside the terminal
F1 · Music · Movies · Side quests
When I'm not staring at decompiled bytecode, I'm usually deep in a completely unnecessary F1 rabbit hole, listening to something on repeat, or picking up a side quest nobody asked for.
Internships and opportunities in cybersecurity, threat intelligence, and applied AI/ML. Happy to talk about malware analysis, agent security, or anything in between.